
Data & Tracking
Third party cookies: what they are, where they disappear and what replaces them

Copy for AI
Third party cookies are cookies set by another domain than the site you visit.
Think of an ad network or an embedded widget loaded on that page. Because the same domain sits on thousands of sites, it can recognise someone across all of them.
The verdict: third party cookies are already gone for Safari and Firefox users, and optional in Chrome. Build your measurement on first-party data and server-side signals, not on what browsers decide next.
They’re being replaced by first-party cookies, server-side tracking and your own customer data.
For marketers, the question is no longer whether they disappear. It’s how dependent your measurement still is on them.
What exactly are third party cookies?
They’re cookies from a domain other than the page you’re on.
A cookie is a small text file a website stores in your browser. Whether it’s first party or third party depends on the domain.
MDN’s definition
MDN, Mozilla’s web documentation, puts it this way in its guide to third party cookies: if the domain and scheme of the cookie differ from the page you’re viewing, it isn’t a cookie from the same site.
It’s then referred to as a third party cookie.
That happens when a page loads content from other domains, such as images, iframes or widgets.
First party vs third party cookies
Here’s the difference side by side:
| First party cookie | Third party cookie | |
|---|---|---|
| Set by | The site you visit | Another domain on that page |
| Example | Your basket, your language choice, the GA4 cookie on your domain | An ad network loaded on many sites |
| Readable by | Only that domain | The external domain, on every site where it loads |
| Typical purpose | Functionality, analytics, your own measurement | Cross-site profiles, retargeting, cross-site measurement |
| Browser blocking | Rarely | By default in Safari and Firefox |
Why they’re under fire
The Belgian Data Protection Authority sums up the risk.
Third party cookies let those parties track browsing behaviour over time and across numerous websites. They then build profiles for targeted marketing.
That’s exactly why they’re under fire.
Which browsers block third party cookies?
Safari, Firefox and Brave block them by default; Chrome doesn’t.
According to MDN’s overview:
| Browser | Default behaviour |
|---|---|
| Safari | Blocks through Intelligent Tracking Prevention, on by default |
| Firefox | Blocks through Total Cookie Protection within Enhanced Tracking Protection, on by default |
| Chrome | Doesn’t block by default, only in Incognito or when the user sets it |
| Edge | Blocks trackers from unvisited sites and known harmful trackers |
| Brave | Blocks tracking cookies by default |
In one picture:
Default settings per browser, based on MDN’s overview, checked 5 November 2026.
What that means for a B2B site
On a B2B site with many iPhone and Mac visitors, measurement that leans on third party cookies has been missing a large share of traffic for years.
Check it yourself: look at your browser split in GA4 to estimate how big that share is for you.
What did Google decide about third party cookies in Chrome?
Chrome keeps them, and lets users choose.
Google announced in 2020 that Chrome would phase these cookies out. It then postponed that several times.
The April 2025 change of course
On 22 April 2025 came the turn. Google’s Privacy Sandbox update says Chrome keeps its current approach of letting users choose.
There’ll be no new standalone prompt. Users keep deciding in Chrome’s privacy and security settings.
What it means for marketers
Three things follow from that:
- Chrome keeps allowing them by default, unless the user blocks them or browses in Incognito.
- Privacy Sandbox gets a smaller role. Google itself wrote that those APIs may play a different role. So don’t build measurement on them.
- The problem hasn’t gone away. Safari, Firefox, ad blockers, cookie law and banner refusals still limit tracking through other domains.
So Chrome’s decision buys you nothing on the other browsers.
What does this mean for your ads and your measurement?
Less than most marketers think: the big platforms already measure on first-party signals.
Many marketers assume their ad measurement runs on third party cookies. With the big platforms, that’s largely no longer the case.
| What you do | What it relies on | Effect of cookie blocking |
|---|---|---|
| Measuring conversions in Google Ads | A first-party cookie on your own domain plus the gclid in the URL | Limited, provided your tags and consent are right |
| Measuring conversions in Meta | The fbp and fbc cookies on your own domain plus the Conversions API | Limited, if you use CAPI |
| Retargeting through ad networks on other sites | Often third party cookies | Smaller audiences in Safari and Firefox |
| Cross-site profiles and data brokers | Third party cookies | Less and less usable |
| Attribution across several channels | A combination of cookies, UTMs and CRM data | Gaps if you rely on cookies alone |
Google Ads runs on your own domain
Here’s a Google Ads conversion action measured on our own site. It counts form sends from our own domain, not from a cross-site cookie:
 The contact form conversion action in our own Google Ads account, October 2026. It runs on our domain and the gclid, not on third party cookies.
How that click ID travels into your CRM is explained in storing the GCLID in your CRM.
Where the real loss sits
The real loss lies less in the platforms and more in three places:
- Retargeting through ad networks on other sites
- Visitors who refuse your cookie banner
- Ad blockers that stop scripts
How to absorb that is in the next section.
What replaces third party cookies?
No single replacement: a set of techniques that together measure better than cross-site cookies ever did.
The six building blocks
- First party data. Data you collect yourself and with consent: forms, CRM, newsletters, customer behaviour. How to build it is in our guide to first party data.
- Server-side tagging. Your tags run through a server on your own subdomain, so cookies are first party and you decide which data goes where. See our guide to server-side tracking, or how hosting works on Stape.
- Conversions APIs. Meta, LinkedIn and TikTok let you send conversions from your server, with a hashed email address instead of a cookie. Read how in our guides to the Meta Conversions API, the LinkedIn Insight Tag and Conversions API and the TikTok Pixel and Events API.
- Enhanced conversions and offline conversions. Google Ads recognises leads through a hashed email address and through CRM imports. See enhanced conversions for leads and importing offline conversions from your CRM.
- Consent Mode v2. Google models conversions of visitors who refuse, based on cookieless signals. See our guide to Consent Mode v2.
- Contextual targeting and your own audiences. Instead of following people across the web, you advertise on context or on your own customer lists. More in cookieless marketing and paid social without cookies.
First-party measurement in practice
First-party analytics keeps working when cross-site cookies don’t. For example, here’s a source report from our own GA4, measured on our own domain:
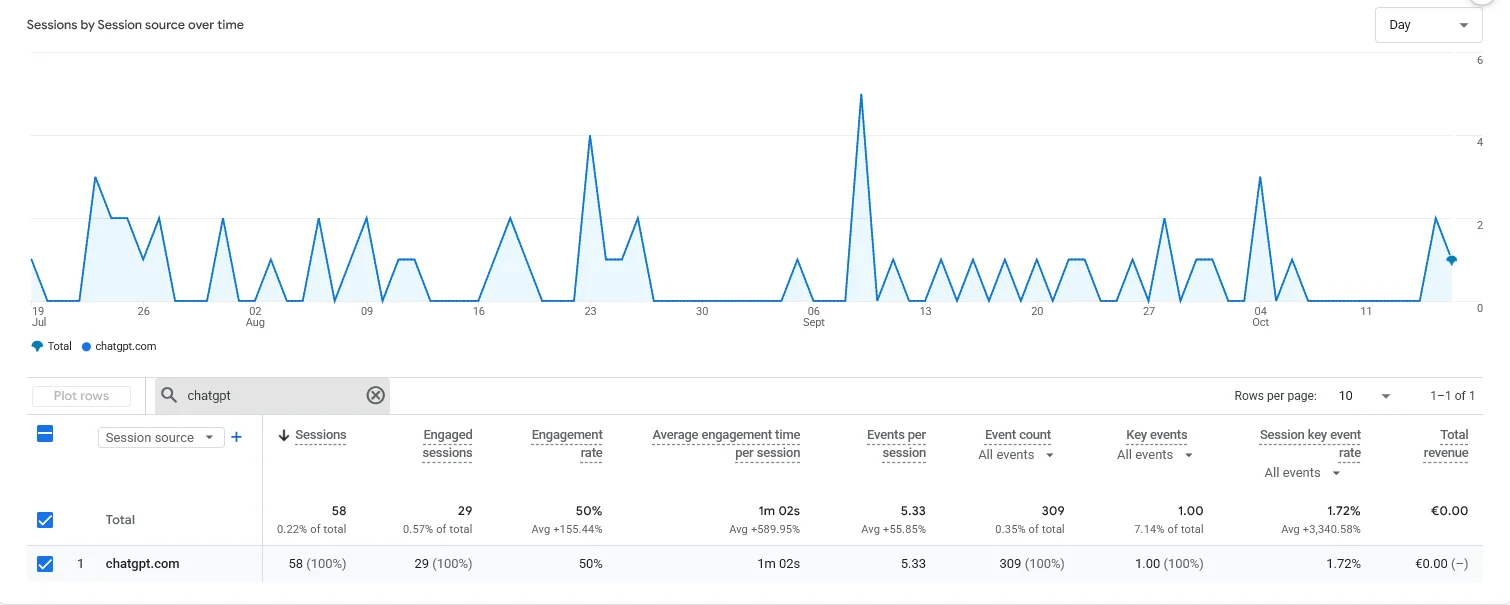 GA4 traffic acquisition in our own account for customerimpact.be, October 2026. First-party measurement: 58 sessions from chatgpt.com in 90 days.
No third party cookie is involved in that number.
Technical alternatives for widget builders
For websites that offer embedded services themselves, there are technical alternatives:
- Partitioned cookies (CHIPS): a separate cookie jar per top-level site
- Storage Access API: cross-site access for a few known sites, with a user prompt
Those are mainly relevant to widget developers, not to your marketing measurement.
How do you check which third party cookies your site sets?
In four checks, from browser to banner.
Step 1: Developer tools
Open your site in Chrome, go to Application and then Cookies. You’ll see per domain which cookies are set.
Anything not from your own domain is third party. Here’s the panel to look at:
Step 2: Your cookie banner scan
A consent management platform scans your site and sorts cookies into categories.
Compare that list with what you actually expect.
Step 3: Test without consent
Refuse all cookies in your banner and look again.
No marketing cookies may appear then, first party or third party.
Step 4: Tag Manager preview
Check which tags fire before and after consent.
An ad tag that fires before someone chooses often sets cookies already.
Clean up what you find
Found cookies from services you no longer use? Clean up the tags.
Old chat widgets, abandoned ad networks and test scripts often stay in place for years. We do this as standard in a tracking audit.
Do you need consent for first party cookies?
Yes, if they serve analytics or marketing.
The Data Protection Authority states that no cookie or tracker may be placed or read without prior information and consent. The only exception is what’s strictly necessary to deliver the requested service.
According to the authority, an analytics cookie doesn’t fall under that exception.
Purpose counts, not the domain
The difference between first and third party doesn’t change that obligation: the purpose is what counts.
Withdrawing consent must be as easy as giving it. In the Netherlands, the Dutch Data Protection Authority (Autoriteit Persoonsgegevens) takes the same line.
Watch out: first party and server-side measurement help against browser restrictions and ad blockers. They don’t help against a refusal in your banner.
Where to read more
How to set up your banner correctly is in cookie banner rules in Belgium.
Which tool to choose is in choosing a consent management platform.
This isn’t legal advice: run your setup past your DPO or lawyer.
Should you allow cookies from other domains in your own browser?
For most people, blocking is a reasonable default.
We get this question a lot too, separate from marketing. Blocking means you’re tracked less across sites.
When blocking breaks something
Sometimes an embedded service stops working, such as a login window or a payment module from an external party.
Chrome then lets you add exceptions per site in its privacy and security settings.
As a marketer: test your own site in both situations, so you know what visitors with strict settings see.
How do you build measurement that doesn’t lean on cookies from other domains?
In six steps, in this order:
- Map which tags and cookies your site sets today.
- Clean up what you no longer use.
- Put a correct cookie banner with Consent Mode v2 in place.
- Build a data layer with fixed events for every form and every appointment.
- Add server-side tagging and send conversions through the APIs of Google, Meta, LinkedIn and TikTok.
- Feed your CRM back, so platforms learn from qualified leads and deals.
What that looks like in practice
Our cases show it.
At Tryve we rebuilt the conversion measurement without noise. At Kaizo we let GA4, Google Ads and Meta steer on the same booked demo.
Want that setup for your own site? Our tracking specialist builds it to measure, on request.
Get in touch for a first check.
For more on privacy-friendly measurement, read our guides on Cookiebot and Matomo.
Frequently asked questions
What is the difference between first party and third party cookies?
First party cookies are set by the site you visit and can only be read by that domain. Third party cookies come from another domain on the page and can recognise you across several sites.
Are third party cookies disappearing in Chrome?
Not according to current plans. In April 2025 Google decided to leave the choice with the user and not to introduce a new prompt. Safari and Firefox do block them by default.
Does Google Ads conversion tracking still work without third party cookies?
Yes. Google Ads measures conversions with a first-party cookie on your own domain and the gclid in the URL. Enhanced conversions and offline conversions make that measurement more robust.
Is server-side tracking a way to bypass cookie consent?
No. Server-side tracking moves the technical route, not the legal obligation. For analytics and marketing purposes you still need prior consent in Belgium and the Netherlands.
How do I see which third party cookies my website sets?
Through your browser’s developer tools (Application, then Cookies) or through the scan of your consent management platform. Cookies from a domain other than yours are third party.
Free website scan
Enter your website and get an automatic scan within minutes, with concrete technical and SEO improvements. No sales pitch.
We only use your details for your scan. No spam, unsubscribe anytime.