
Website & Development
SSL Certificate and HTTPS: Why Your Website Really Needs It

Copy for AI
An SSL certificate is a small file that encrypts traffic between visitor and website.
It makes your web address start with https instead of http. The browser then shows a padlock instead of a warning.
The verdict: for a B2B website, an SSL certificate isn’t a technical detail but a trust requirement. Without one, visitors get spooked right before they fill in your contact or quote form.
The good news: it’s usually free. The work sits in setting it up correctly.
Below: what it does, why HTTPS matters, and how to get one.
What is an SSL certificate exactly?
A digital file that does two things: it encrypts the connection, and it confirms your website is who it claims to be.
SSL stands for Secure Sockets Layer.
Technically, modern sites use its successor, TLS (Transport Layer Security). In practice almost everyone still calls it “SSL”.
Job 1: encryption
Encryption makes everything travelling between visitor and website unreadable to anyone watching the network.
For example, someone enters their name, company, email address and phone number on your contact page. That data travels across the internet as gibberish, not as plain text.
Watch out: without a certificate, someone on the same wifi network can in principle read that data along the way.
Job 2: identity
The certificate is issued by a trusted party, a Certificate Authority.
The browser checks that certificate automatically on every visit:
- Valid: the padlock appears
- Invalid or expired: the browser shows a warning
- Missing: the page is marked “Not secure”
Here’s where you see it in Chrome. Click the icon left of the address:
That popup is the browser’s verdict on your certificate, in plain words for every visitor.
The whole check in one picture
It all happens in a fraction of a second, before the page loads:
If any step fails, the visitor sees a warning instead of your page.
What is the difference between HTTP and HTTPS?
HTTPS is simply HTTP with encryption on top.
That single letter S makes the difference between a secure and an insecure connection.
Same conversation, different tunnel
HTTP (HyperText Transfer Protocol) is how your browser and a website talk to each other.
With plain HTTP, that happens unprotected. With HTTPS, exactly the same conversation takes place inside an encrypted tunnel that the SSL certificate sets up.
How visitors see the difference
You recognise it immediately in the address bar:
| HTTP | HTTPS | |
|---|---|---|
| Address starts with | http:// | https:// |
| Browser shows | ”Not secure” | A padlock |
| Form data travels | As plain text | Encrypted |
| Visitor reads it as | ”Something is wrong here” | Nothing, it’s the norm |
That “Not secure” message isn’t a small grey line of text. It’s a clear signal that the average visitor reads as “something is wrong here”.
HTTPS became the default in 2018
Since Chrome 68 in July 2018, Google Chrome has marked all plain HTTP pages as not secure. The other browsers followed.
HTTPS has since become the default on the web.
So a B2B site without HTTPS no longer looks neutral. It looks suspicious.
Why is HTTPS important for trust?
Because a visitor who doubts your security doubts your entire company.
In B2B, no one buys on impulse. Your visitor weighs up whether you’re a reliable partner for a project that runs for months or years.
A “not secure” warning in the address bar is exactly the wrong first signal.
The warning works subconsciously
Few people know what an SSL certificate technically does.
But almost everyone senses that a red or crossed-out padlock is bad news.
That undermines all the other effort you’ve put into building trust on your B2B website: your references, your case studies, your clear language.
One insecure connection can undo all of that in a second.
A padlock isn’t a seal of quality
Important to be clear about: a padlock doesn’t prove that a company is trustworthy.
It only proves that the connection is encrypted. Even an untrustworthy site can have a valid certificate.
Rule of thumb: HTTPS isn’t a seal of quality, but its absence is a direct reason to leave.
Our guide to website security covers the layers on top.
See HTTPS as the foundation your credibility stands on.
What does SSL mean for your B2B lead forms?
It’s indispensable: without encryption, you ask people to send their data over an unsecured line.
Every form on your site transmits personal data. Think of a contact request, a quote request or a download behind a form.
Encryption and the GDPR
Under the GDPR, you’re required to protect that data appropriately. Encryption during transport is a logical part of that.
Our checklist for a GDPR-compliant contact form lists the other parts.
The conversion angle
There’s also a purely practical conversion angle.
Some browsers show an extra warning as soon as you type into a data field on an unsecured page.
Picture it: a visitor is finally ready to get in touch, starts typing, and gets a pop-up saying the page isn’t secure. That lead is gone.
All your work on a smooth, convincing contact page that generates leads is then for nothing.
The silent base layer
HTTPS is the silent base layer under every form of conversion optimisation of your forms.
You can endlessly tinker with field order, button text and the number of questions.
But if the connection isn’t secure, you leak leads. And you don’t even see it happen.
Does an SSL certificate also help for SEO?
Yes, but keep your expectations realistic: HTTPS is a light ranking factor, not a magic bullet.
What Google said in 2014
Google announced HTTPS as a ranking signal in August 2014.
It called it “a very lightweight signal” that affected fewer than 1% of global queries. It carried less weight than high-quality content.
That’s still the right way to look at it.
The indirect SEO gain is bigger
The real SEO gain lies less in that direct signal and more in the consequences around it:
- a “not secure” mark drives visitors away
- high bounce rates and low engagement don’t help your rankings
- HTTPS is a condition for several modern browser techniques
It also gives a clean, professional impression to everyone who links to your site. HTTPS is one of the basics in any technical SEO check.
The switch is a migration
Do watch out for one pitfall.
Google lists the move from HTTP to HTTPS as a site move with URL changes. It advises permanent redirects, kept for at least a year, and warns of temporary ranking fluctuation.
The approach needs the same discipline as any website migration without losing rankings: map everything out, redirect neatly and check afterwards.
Start with the pages that have links
Start your redirect list with the pages other sites link to. Search Console shows them in the Links report:
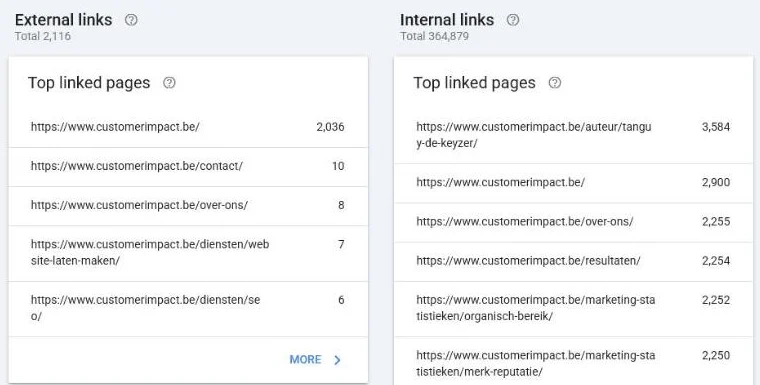 The Links report in our own Search Console for customerimpact.be, October 2026. Pages with external links go to the top of the redirect list.
A 301 redirect plan turns that list into rules.
Then test old URLs with our free redirect checker.
How do you get an SSL certificate on your website?
In most cases it’s free and arranged via your hosting, so cost is rarely the barrier anymore.
Free certificates via Let’s Encrypt
Many hosting providers automatically supply a free certificate via an initiative like Let’s Encrypt.
It issues recognised certificates at no charge, and all the major browsers trust them. Let’s Encrypt says some hosts add a small administrative fee on top.
Good enough? For a standard B2B website, such a free certificate is as a rule perfectly sufficient. Our guide to choosing web hosting shows what else to check in a host.
Three points of attention
Check these three after setup:
- Automatic renewal: certificates expire, so renewal must run by itself
- Full coverage: main domain, www variant and every page on https
- Correct redirects: a permanent redirect from http to https
On renewal: Let’s Encrypt certificates are valid for 90 days by default, or six days if you opt in to short-lived ones. Most hosts renew automatically, but check that the setting is active.
On coverage: a single image or script that still loads via http can trigger a mixed-content warning.
On redirects: without a permanent redirect, old links and bookmarks land people on an insecure version.
When a paid certificate makes sense
Paid certificates with extended identity verification also exist. Let’s Encrypt only issues domain validation certificates and has no plans for OV or EV ones.
They can be relevant for large organisations with strict requirements. For most B2B companies, that’s overkill.
Our advice: don’t buy an expensive certificate because it sounds impressive, if a free variant delivers exactly the same padlock and encryption.
How do you switch an existing site to HTTPS?
In six steps, in this order, so no visitor or ranking falls through the cracks.
Step 1: install the certificate
Activate it in your hosting panel, or ask your host to do it.
Check: both yourdomain.be and www.yourdomain.be are covered.
Step 2: fix mixed content
Search your pages for images, scripts and fonts that still load over http.
Change them to https, or to relative paths.
Step 3: redirect every http URL
Set a permanent 301 redirect from each http address to its https twin.
Watch out: avoid redirect chains such as http to http://www to https://www. One hop is enough.
Step 4: update your own references
Point internal links, canonical tags and your XML sitemap at the https URLs.
Otherwise you keep sending Google and visitors through the redirect.
Step 5: add the https property in Search Console
Make sure you see the https version in Google Search Console. A Domain property covers both protocols at once.
Step 6: monitor for a few weeks
Watch your indexed pages, 404s and form submissions.
A short dip is normal during a site move. A lasting drop points at a missed redirect.
Frequently asked questions
Is SSL the same as TLS?
Practically, yes. TLS is the modern successor of SSL, but almost everyone still calls the certificate “SSL”.
Is a free SSL certificate safe enough?
For a standard B2B website, yes. A free Let’s Encrypt certificate gives the same padlock and encryption as a paid one; paid OV or EV certificates add identity checks, not stronger encryption.
How long is an SSL certificate valid?
Let’s Encrypt certificates last 90 days by default, or six days for short-lived ones. Make sure your host renews them automatically.
Will switching to HTTPS hurt my rankings?
Only if you skip the redirects. Google treats HTTP to HTTPS as a site move: use permanent redirects, keep them at least a year and expect a short fluctuation.
The short summary
An SSL certificate encrypts the connection, turns your address into HTTPS and shows a padlock instead of a warning.
Why it’s a baseline
For a B2B site, that’s a baseline requirement. It protects your lead form data, keeps trust intact when someone wants to get in touch, and gives a light SEO bonus.
Cost: usually zero, because good hosting arranges it for free.
The real attention lies in the execution: full coverage, automatic renewal and neat redirects, especially when you switch from an existing HTTP site.
Next step: want a website that’s secure, fast and built for leads? See our approach to professional website development, or read the complete guide to B2B website development.
Free website scan
Enter your website and get an automatic scan within minutes, with concrete technical and SEO improvements. No sales pitch.
We only use your details for your scan. No spam, unsubscribe anytime.