
Website & Development
IT and MSP website: proving SLAs, ISO certification and security

Copy for AI
An MSP website convinces with proof, not with technology promises.
That proof is concrete SLAs, a demonstrable ISO 27001 scope, honest uptime figures and references a buyer can verify.
The verdict: a risk-averse buyer is outsourcing critical infrastructure and mainly wants to know what happens when things go wrong. Your IT company website has to answer that before anyone asks for a quote.
Here’s how to turn SLAs, security and certifications into trust signals that lower the barrier to enquire.
Why is buying IT a risk decision?
Because whoever outsources their network, backups or cloud management hands control to a partner for months or years.
The buyer who lands on your site quietly asks three questions:
- will my systems keep running?
- who is liable in an incident?
- is my data safe?
Your B2B website has to answer those questions before anyone requests a quote.
The broader framework is in our guide to building a B2B website.
Which trust signals convince a risk-averse IT buyer?
The ones a buyer can check.
Vague reassurance backfires with a technical audience used to seeing through marketing language.
The four layers that weigh heaviest
For anyone outsourcing critical IT, four things decide:
- Continuity: what you promise on availability and response time, and the counterpart if you miss it.
- Security: how information security is safeguarded, shown by a certificate or audit.
- Liability and governance: who is responsible, how escalation works, how you report incidents.
- References: whether others in a similar situation work with you and will confirm it.
Proof beats design
The difference between a site that converts and one that loses buyers rarely lies in the design.
It lies in whether these four layers are solid. That’s the logic of building trust on a B2B website: proof beats persuasion.
Other risk-averse sectors work the same way. For example, a healthcare website that makes its medical authority and E-E-A-T demonstrable.
How do you make an SLA concrete on your website?
Name the figures a buyer can hold you to.
“High availability” says nothing. “99.9% guaranteed uptime with a four-hour response time on critical incidents” says everything.
What to show on your SLA page
Make clear what you actually promise, not just that you have an SLA:
- Availability level: a hard percentage, translated into downtime.
- Response and resolution times: per priority, including an outage at three in the morning.
- Service windows and support: office hours or 24/7, and through which channels.
- Missed commitments: service credits or an escalation procedure.
Translate percentages into hours
99.9% uptime works out to roughly 8.8 hours of downtime per year. 99.99% means just under an hour.
Showing that translation proves you understand the impact on a client:
The same maths for four common SLA levels, based on 8,760 hours in a year:
| Uptime | Downtime per year | Downtime per month |
|---|---|---|
| 99.5% | about 43.8 hours | about 3.7 hours |
| 99.9% | about 8.8 hours | about 44 minutes |
| 99.95% | about 4.4 hours | about 22 minutes |
| 99.99% | about 53 minutes | about 4 minutes |
Tip: put this table on your SLA page next to the level you sell.
You don’t publish the whole contract
The goal is that after reading your SLA page, a buyer thinks: this partner knows exactly what they’re signing up for.
That’s a direct link between your offering and the willingness to get in touch.
Which commitments to set with your own supplier: website maintenance contract and SLA. For the clauses themselves, see what belongs in a website contract SLA.
What does ISO 27001 mean, and how do you show it credibly?
ISO 27001 is the international standard for information security.
A certificate proves you run a managed system, an ISMS, to control security risks, tested by an independent party.
Which version counts
The current version is ISO/IEC 27001:2022, which replaces the 2013 edition.
Certification bodies had to move certified clients to the 2022 edition by 31 October 2025. A 2024 amendment added climate-related provisions.
So a logo alone says little. The details decide whether it comes across as credible.
What a critical buyer checks
Show the mark plus the context:
- Scope: which services and locations the certificate covers.
- Certification body and date: so it’s verifiable and current.
- The certificate itself: a downloadable document, not just an image.
Watch out: ISO 27001 covers a defined part of an organisation. A buyer who finds the scope too narrow will ask.
No ISO 27001 yet? Show what you do have
Be honest about it, then show what’s in place.
In Belgium, the CyberFundamentals framework (CyFun) from the Centre for Cybersecurity Belgium is a recognisable alternative. It makes security demonstrable in a structured way.
CyFun was originally developed in Belgium and builds on the NIST Cybersecurity Framework, with three assurance levels: Basic, Important and Essential.
NIS2 raises the stakes
Belgium transposed the NIS2 directive through the Act of 26 April 2024, in force since 18 October 2024.
It imposes concrete security and reporting duties on many IT service providers and their clients.
Verified or certified CyFun, or ISO 27001 aligned with it, gives a presumption of conformity with the NIS2 security requirements.
Showing that you know this is a trust signal in itself.
How do you prove uptime and security without empty claims?
With proof a buyer can see for themselves.
A figure only you report weighs less than one that’s externally verifiable.
A public status page
Show current and historical uptime on a public page.
That’s more transparent than a percentage in your sales copy. It shows you have nothing to hide.
Here’s what a public status page looks like:
Audits, tests and measures in plain language
Three more ways to make security tangible:
- Third-party audits and penetration tests: referenced, without confidential details.
- Concrete measures: how you handle things such as backups, recovery and access.
- Data location and contracts: where data sits and who processes it.
For a technical buyer this isn’t noise. It’s exactly what they want to read.
Data location also ties into the GDPR. Our guides on EU hosting and data residency and the data processing agreement cover the paperwork side.
Structured data for search and AI
Where possible, add structured data so search engines and AI assistants pick up your certifications and details correctly.
How that works: schema markup. You can check the result in a validator:
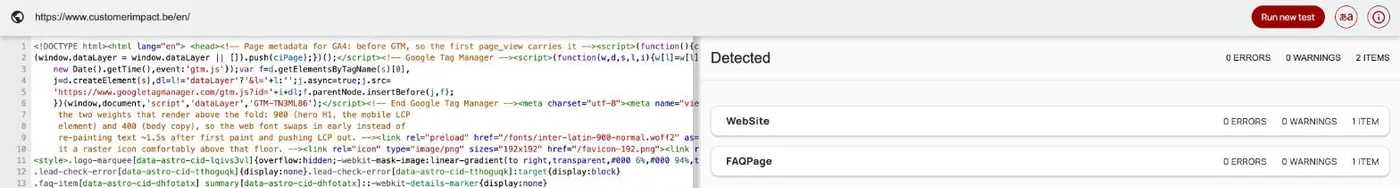 The Schema Markup Validator on our own English homepage, October 2026. Check that each detected type matches what the page visibly says.
Be realistic about 100%
No provider achieves 100% uptime. Pretending otherwise undermines your credibility.
An honest figure with context convinces an experienced buyer more than a perfect claim.
What role do references and the right page structure play?
References prove your promise holds up in practice.
A case study showing how you resolved an incident or ran a migration without downtime beats a wall of client logos.
Make references verifiable
A real name, role and company weigh more than an anonymous quote.
Ask clients in comparable sectors, such as another logistics firm for a logistics prospect. Recognition lowers the perceived risk. That’s social proof a buyer can trust.
Public review profiles add a third-party layer:
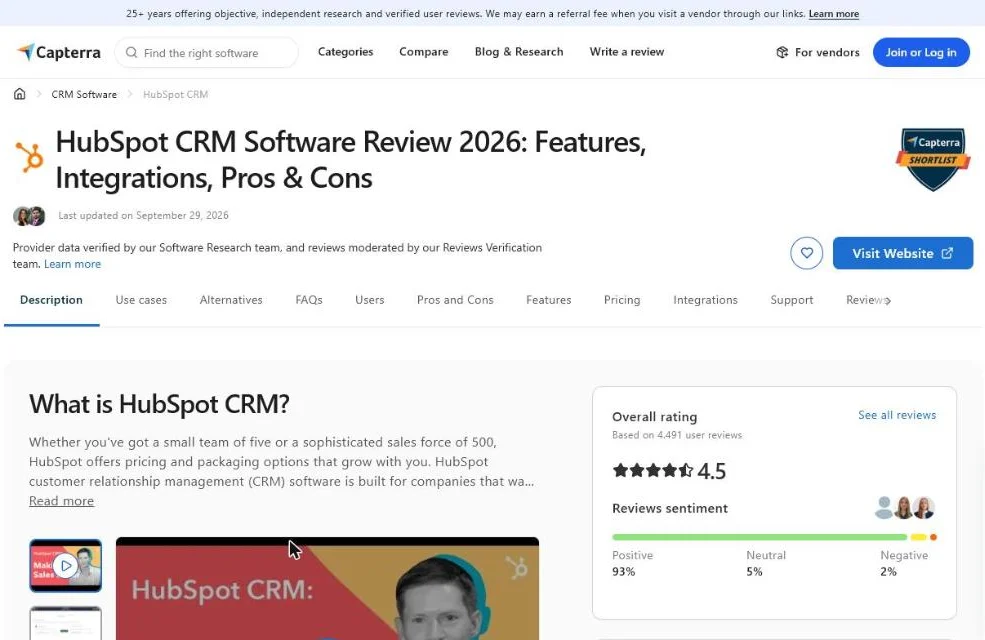 A public Capterra profile, October 2026: rating and review count show a prospect whether the promise holds.
Put proof where the decision falls
Don’t hide your SLA and certifications in the footer. In practice:
- Near the form: strongest trust signals next to your contact form, as in contact page optimisation.
- About page: team, certifications and approach, as in an about page that generates leads.
- Own pages: SLAs and security each on a separate page, findable for buyers and AI assistants.
Platform comes second
Webflow, WordPress or headless: it’s the proof and structure that decide whether a buyer clicks through.
On WordPress, make sure AI search engines pick your site up: make WordPress AI-proof for citations.
Keep it patched with our WordPress security guide.
Frequently asked questions
What should an MSP website show about its SLA?
The availability percentage, what it means in downtime, response and resolution times per priority, support hours and what happens when you miss a commitment.
How much downtime is 99.9% uptime?
About 8.8 hours per year, or roughly 44 minutes per month. At 99.99% it drops to about 53 minutes per year.
Is a logo enough to show ISO 27001 certification?
No. Show the scope, the certification body, the certification date and the certificate itself, so a buyer can verify it.
What if my IT company has no ISO 27001 certificate?
Say so honestly and show what you do have. In Belgium, CyberFundamentals (CyFun) is a recognised, structured way to make security demonstrable.
The short summary
An IT company or MSP website convinces by making certainty demonstrable.
Translate SLAs into hard figures and show ISO 27001 or CyFun with scope and date. Prove uptime with a status page and place verifiable references near the decision.
The core: buyers don’t walk away over your technology. They walk away over doubt about what happens when things go wrong.
Remove that doubt and you lower the barrier more than any redesign could.
Want your SLAs, security and references turned into a site that generates leads? See our website development or contact us for a first look at your current pages.
Free website scan
Enter your website and get an automatic scan within minutes, with concrete technical and SEO improvements. No sales pitch.
We only use your details for your scan. No spam, unsubscribe anytime.