
Website & Development
WordPress Hacked? A Step-by-Step Plan to Restore and Secure Your Site

Copy for AI
If your WordPress site is hacked, isolate it first and delete nothing in a rush.
Then work in a fixed order: back up the infected state, clean up, restore a clean version and only re-secure at the end.
The verdict: a hacked WordPress site is fixed by replacing files, not by hunting for bad lines until it “works again”. That approach misses the backdoor the attacker uses to come back.
Below is the full step-by-step plan, how to get the Google warning removed and how to stop it happening again.
How do you know for sure your WordPress is hacked?
You know through a few recognisable signals, and most of them are visible from the outside.
WordPress’s own FAQ for hacked sites calls these “Indicators of Compromise”. The common ones are:
- visitors get redirected to spam, gambling or dubious sites
- your homepage is defaced
- unknown admin accounts appear in your dashboard
- Google Search Console sends a notice about hacked content
- your host disables the site or flags it for malware
The subtle signs
Sometimes it’s quieter. Your site is suddenly slow, or your host warns you about suspicious traffic.
Or your rankings collapse. Google found hidden spam pages that you can’t see.
Visitors may also complain that their antivirus flags your site. That’s a signal too.
How to check it yourself
View your site in a clean browser while logged out, and search for your domain in Google.
Hidden spam (the so-called “SEO hack”) is often only visible to search engines, not to the logged-in administrator.
The cURL test
Quick test: request your homepage and a few existing URLs with a tool like cURL. Check whether there’s code or there are links in it that you didn’t put there.
For example, a footer full of links to pharmacy or casino sites you’ve never heard of is a classic SEO hack.
Not every glitch is a hack
Stay realistic. Not every error is an attack.
A white page or an error message after an update is usually a plugin conflict, not a break-in.
Our guide to too many WordPress plugins explains why those conflicts happen.
Rule of thumb: first establish what’s really going on, then act. Deleting things in a panic destroys the evidence.
What is the first step when your WordPress is hacked?
The first step is to isolate the site and delete nothing in a rush.
Put WordPress into maintenance mode or take the site temporarily offline. Visitors and Google then stop receiving infected pages, and the damage doesn’t grow.
Then do the following, in this order, before you clean anything up.
Make a full backup of the infected state
It sounds odd. But you want to preserve the files and the database exactly as they are now.
You need them to investigate. And if a cleanup goes wrong, you can go back.
WordPress’s FAQ for hacked sites recommends exactly this snapshot before you start cleaning, “even if it’s infected”.
Collect evidence
Note when you discovered it, which notifications you received and what’s visibly wrong.
The WordPress FAQ calls this the baseline of an incident report. It also asks what changed recently: a new plugin, a theme edit, a widget?
Server logs: keep the logs from your hosting. They often contain the time and the entry point of the attack.
Notify your hosting provider
On a shared server your infection can affect other sites, and the other way around.
Many hosts can help with logs, a scan or a temporary quarantine.
Watch out: a hacked site that sends spam can get your server’s IP blacklisted, and that can hit your business email too, as the WordPress FAQ warns.
Scan your own computer
The infection doesn’t always start on the server. Sometimes it starts at your desk.
The WordPress FAQ says attackers often run trojans on a local laptop or desktop to sniff FTP and wp-admin logins. So run a full malware scan on every machine that logs in to the site.
Don’t change the content yet
It’s tempting to immediately delete that one odd line. But without an overview, you only make the investigation harder.
Isolated and backed up? Then you’re ready to clean.
How do you thoroughly clean a hacked WordPress site?
You clean up by replacing infected components with clean originals, not by endlessly hunting for suspicious code.
That’s how you make sure you don’t overlook anything.
Work through these six steps systematically.
Step 1: Scan the entire installation
A security scanner such as Wordfence, Sucuri or MalCare searches your files and database for known malware and modified core files.
Use it as a compass: not as the only truth. The WordPress FAQ itself says no single scanner is the best approach, but combining an application scanner with a remote one improves your odds.
Step 2: Replace the WordPress core
Download a fresh copy of the same WordPress version from WordPress.org. The download sits right on the homepage:
 WordPress.org, October 2026. Download the exact version your site runs, not simply the latest one.
Fully restore the core folders (wp-admin and wp-includes) and the individual core files in the root.
Same version: the WordPress FAQ warns that an older or newer version is “likely to kill your website”. Update only once the site is clean.
Upload over SFTP, not with the reinstall button
Use SFTP rather than the reinstall button in wp-admin. That installer only overwrites existing files, and hacks often add new ones.
Don’t edit infected files by hand. Replacing is safer. It’s faster too.
Step 3: Reinstall plugins and themes
Remove every plugin and every theme and reinstall them from the official source.
Software you can no longer download anywhere (expired or “nulled” plugins) goes in the bin for good. That’s often exactly where the leak is.
Our list of WordPress plugins for B2B sites helps you decide which ones you really need back.
Step 4: Check the suspicious places
Look specifically for injected code and redirects in these files:
wp-config.php.htaccess, the file the WordPress FAQ calls one of the most abusedindex.php- your theme’s
header.php,footer.phpandfunctions.php
In the database, watch the wp_users and wp_options tables.
Version control: if your site lives in Git or SVN, a diff against the official files shows every change in seconds.
Step 5: Remove unknown admin accounts and rogue cron jobs
A leftover administrator or scheduled task is the way an attacker comes back after you’ve cleaned up.
So check every admin user and every scheduled task. Remove what nobody can explain.
Step 6: Reset all passwords and keys
Reset all WordPress logins, your database password, FTP/SFTP, the hosting panel and the secret keys (salts) in wp-config.php.
New salts log out everyone who’s still signed in, including the attacker. Assume everything the attacker could see has been compromised.
Then change the passwords again once the site is clean, as the WordPress hacked-site FAQ advises.
When to call in a professional
Not sure you’ve really caught it all? With a deep or repeated infection, professional malware removal isn’t a luxury.
A half-cleaned site that’s reinfected a week later costs you more. Do it properly once.
How do you restore your site and get the Google warning removed?
You restore in one of two ways: roll back to a clean backup from before the hack, or thoroughly clean the current site as described above.
Backup or cleanup: which route?
An older, guaranteed clean backup is often the fastest and most reliable route. But only if you know it dates from before the break-in.
Use this table to decide:
| Your situation | Best route | Why |
|---|---|---|
| Clean backup from before the hack, date known | Restore the backup | Fastest, and nothing infected comes back |
| Backup exists, but the hack date is unknown | Clean the current site | The backup may already be infected |
| No usable backup | Clean the current site | It’s the only option left |
Whichever route you pick, still replace the core and reset every password afterwards.
Getting the “this site may be hacked” warning removed
Was your site flagged by Google with “this site may be hacked”? Then you solve it like this:
- Check the Security Issues report in Google Search Console to see what Google found, with example URLs.
- Make sure every reported issue is genuinely resolved. Test the example URLs again and confirm they’re clean.
- Click Request review and explain the problem, the steps you took to fix it and the result.
You’ll find the report in Search Console under Security & Manual Actions, then Security issues. A clean property looks like this:
New to the tool? Our guide to Google Search Console walks through every report.
Only request a review once you’re certain
Google’s Security Issues report documentation is clear: fixing the issue on just some pages won’t earn you a partial return to search results.
It also asks you not to resubmit before you get a decision, because that can mean a longer turnaround for the next request.
How long does Google’s review take?
Timing: for hacked spam, malware and phishing alike, Google says a review can take from a few days to a few weeks.
So be patient. Use that time to get your security in order.
Watch your rankings after recovery
Hidden spam and a security warning can temporarily hurt your organic positions.
Compare clicks and impressions in the Performance report across the date of the hack:
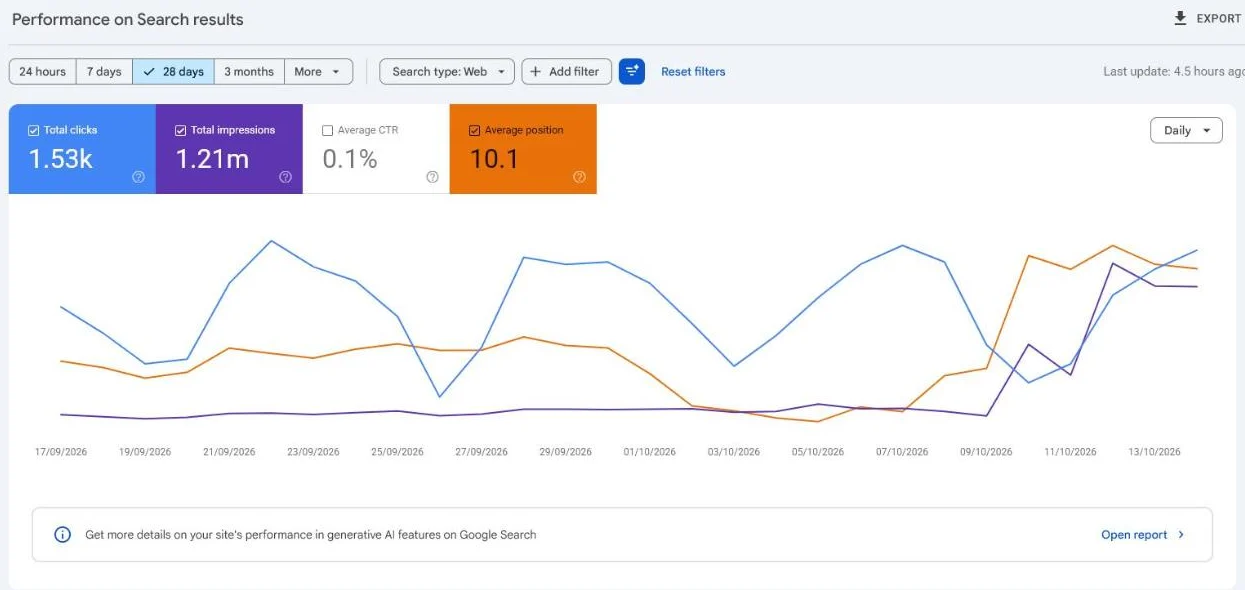 Our own Search Console for customerimpact.be, last 28 days, October 2026. A hack shows up as a sudden break in the clicks line.
Our step-by-step guide to analysing a traffic drop shows how to read that break.
Rebuilding looks a lot like what we describe in keeping your rankings after a website redesign.
The broader basics are in our WordPress SEO checklist.
How do you prevent WordPress from being hacked again?
You prevent it with structural security, because most hacks aren’t sophisticated attacks.
They’re the result of neglected maintenance: an outdated plugin, a weak password or a missing backup.
Want to cover this fully? Then work through our WordPress security checklist with 12 measures.
Where the vulnerabilities sit
Attackers mainly exploit known vulnerabilities, and those sit almost entirely outside core.
Patchstack counted 11,334 new WordPress vulnerabilities in 2025, 91% in plugins and 9% in themes. Only 6 were in WordPress core.
Here’s how those 11,334 break down:
Updating on time closes most doors, but not all of them: 46% had no fix from the developer at public disclosure.
Speed matters: Patchstack puts the weighted median time to mass exploitation of heavily targeted flaws at 5 hours. About half of high-impact vulnerabilities were exploited within 24 hours.
The six measures that close most doors
This is the foundation:
- Keep everything up to date: WordPress core, plugins and themes.
- Shrink your attack surface: remove what you don’t use, replace abandoned plugins.
- Turn on two-factor authentication (2FA): a guessed password alone won’t get anyone in.
- Limit admin rights: strong, unique logins, and clean up old users.
- Automate tested backups: stored away from your server.
- Deploy a firewall or security plugin: it blocks known attack patterns.
Why each one matters
Attack surface: every component you don’t have can’t be hacked either.
Backups: store them separately from your server and test now and then whether you can actually restore them. A backup you can’t restore isn’t a backup.
Firewall: it blocks suspicious traffic and known attack patterns before they reach your site.
HTTPS: a valid certificate doesn’t stop a hack, but it protects every login in transit, as our page on the SSL certificate explains.
Maintenance is a rhythm, not an action
Security isn’t a one-off project. It’s a rhythm. Think of a monthly routine of updates, checks and restore tests.
Our guide to WordPress maintenance lists what belongs in that routine. And what WordPress maintenance costs helps you budget for it.
Prefer to hand it off? Our website maintenance services cover updates, backups, security and uptime monitoring as a fixed plan.
Or step away from plugin maintenance
Our experience: WordPress, Drupal, Webflow and Joomla all used to be really good, and now it depends on the company.
AI and digital-native companies are moving to agentic websites: no plugin updates, no security warnings, and fast updates. That’s what we build with AI website development.
How we build sites that stay secure
At our web design agency we build sites that not only convert but also stay manageable and secure, on WordPress or on another platform that fits your situation.
Which choice is right depends on your team, your content and your growth plans, as we explain in the B2B website guide.
Our piece on when to use WordPress helps you weigh it.
Frequently asked questions
How long does it take to fix a hacked WordPress site?
The cleanup depends on how deep the infection goes. If Google flagged the site, its review of the security warning can then take from a few days to a few weeks.
Can I just restore a backup?
Yes, if you’re sure the backup dates from before the break-in. If you don’t know when the hack started, clean the current site instead.
Should I reinstall WordPress from the dashboard?
No. Upload clean wp-admin and wp-includes folders over SFTP. The dashboard reinstaller only overwrites existing files, and hacks often add new ones.
Does a hack hurt my Google rankings?
It can. Hidden spam pages and a “this site may be hacked” warning can temporarily cost positions and clicks, so monitor Search Console after recovery.
The short summary
You restore a hacked WordPress site in a fixed order: isolate, back up the infected state, then clean up.
Clean by replacing files instead of deleting them. Remove unknown admins and tasks, reset all passwords, and only then request a review in Search Console.
But the real work starts after recovery. That’s where most sites slip. Without updates, strong logins with 2FA and tested backups, you’ll be back in the same place before you know it.
A site you trust is also a site that keeps delivering leads.
Need help cleaning up, restoring or structurally securing your WordPress site? Contact us and we’ll start with a look at what’s infected.
Free website scan
Enter your website and get an automatic scan within minutes, with concrete technical and SEO improvements. No sales pitch.
We only use your details for your scan. No spam, unsubscribe anytime.