
Website & Development
Website Privacy Policy and Cookie Statement: What Must Be Included

Copy for AI
A website privacy policy is really two documents: a privacy statement and a cookie statement.
The privacy statement explains which personal data you collect, why and for how long. The cookie statement describes which cookies and trackers you place.
The verdict: a privacy policy for your website only works if it describes what your site actually does. A pasted generator text fails that test, legally and with buyers.
Many B2B companies lump the two documents together, or paste a free generator text at the bottom of their site.
That exposes them to both a legal and a trust risk.
What is the difference between a privacy statement and a cookie statement?
A privacy statement covers all the personal data you process.
A cookie statement deals specifically with what’s stored or read on your visitor’s device.
These are two documents, each with its own legal basis.
Confusing them is a common mistake.
The privacy statement: GDPR
The privacy statement falls under the GDPR (the General Data Protection Regulation). It governs every processing of personal data, for example:
- a completed contact form
- a newsletter sign-up or a quote request
- job applications
- your CRM
In it you explain who you are, what you do with that data and what rights someone has.
The cookie statement: ePrivacy
The cookie statement, on the other hand, falls under the ePrivacy rules.
In Belgium they’re now anchored in Article 10/2 of the Data Protection Act of 30 July 2018, as the Belgian Data Protection Authority’s cookie checklist notes.
Not only cookies
These rules aren’t only about personal data.
They’re about placing and reading information on the visitor’s device.
That includes more than cookies:
- pixels
- local storage
- fingerprinting
So non-essential cookies need prior consent. That holds even if they contain little personal data.
In short: one document describes what you do with data.
The other describes what you place, and on what basis.
What must your privacy statement contain?
Your privacy statement must tell a visitor, in clear language, who you are, which data you process, why, on what legal basis and what they can do about it.
The seven elements
Article 13 of the GDPR lists these information obligations concretely. A complete privacy statement usually contains at least these elements:
| Element | What to write |
|---|---|
| Data controller | Company name, company number and contact details, plus those of any data protection officer |
| Personal data | Which data you collect and through which channels (forms, email, analytics, customer management) |
| Purposes | For example drawing up a quote, answering a question or invoicing |
| Legal basis | Per processing activity: consent, performance of a contract, a legal obligation or a legitimate interest |
| Recipients | Processors such as your hosting, email tool, CRM or analytics provider, and whether data leaves the EU |
| Retention | How long you keep it, or which criterion you apply |
| Rights | Access, rectification, erasure, restriction, objection, data portability, withdrawing consent at any time and lodging a complaint with the supervisory authority |
Data leaving the EU deserves a closer look.
Our guide to EU hosting and GDPR data residency explains what to check.
Clear language is a legal requirement
Style matters too. Article 12 of the GDPR asks for information “in a concise, transparent, intelligible and easily accessible form, using clear and plain language”.
The same article sets a deadline.
When someone uses one of their rights, you must answer within one month of receipt of the request.
Tip: name one mailbox for those requests in your statement, and make sure someone reads it.
Every element must match your site
That seems like a lot.
But the point is that every element must match what your site actually does.
For example:
- Quote form and newsletter: both must be in it.
- No webshop: payment information doesn’t belong in it.
A privacy statement isn’t a template you fill in.
It’s an honest description of your own data flows.
Your CRM is usually the biggest processor on that list:
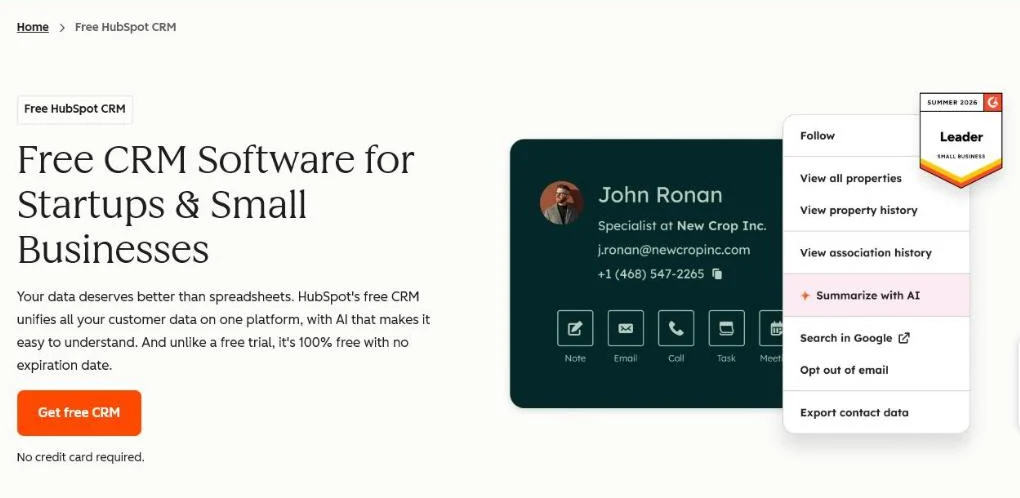 HubSpot’s free CRM page, October 2026. Whatever CRM your forms feed, name it as a processor.
Want the full picture of what a compliant site needs?
Read our guide to a GDPR compliant website.
What belongs in your cookie statement and cookie banner?
Your cookie statement must make clear, per cookie or category:
- which ones you place
- what they’re for
- who places them
- how long they stay
And your banner must ask for valid consent before anything non-essential is loaded.
What the Belgian DPA expects
The Belgian Data Protection Authority has formulated clear expectations about this.
Concretely, the DPA cookie checklist asks among other things:
- No pre-ticked boxes in any layer.
- “Reject all” on the same layer as “accept all”, displayed the same way.
- Not enough: a “settings” button next to “accept all”.
In the first layer, visitors must immediately understand what you’re asking consent for.
Withdrawing must be as easy as giving
Withdrawing consent must be as easy as giving it.
For example, through a clearly visible link to the cookie settings.
Watch out: a banner that only shows “Accept”, or only lets you through once you accept, doesn’t comply.
Our guide to cookie banner rules in Belgium goes through each requirement.
Comparing consent tools? See Cookiebot vs Usercentrics vs Complianz.
Essential or not
Important in practice: essential cookies may be placed without consent.
For example, for a shopping cart or to remember a logged-in session.
For these you do need prior consent:
- analytics
- marketing pixels
- embedded third-party content
The Belgian DPA states that counting visitors is in principle not strictly necessary. Session recording tools such as Microsoft Clarity fall in that same non-essential group:
 Microsoft Clarity’s homepage, October 2026. Heatmaps and recordings are analytics, so they wait for consent.
Running Google Analytics?
Our guide to Google Analytics and the GDPR covers the specifics.
Where the build and the text meet
That has a direct technical consequence.
Your tracking scripts may only fire after the visitor has consented.
If your consent banner is built in incorrectly, those scripts load anyway.
Then your consent is worthless.
This is precisely where the build of your site and your legal text come together, and where things often go wrong. Consent Mode v2 is how Google tags respect that choice.
You can check what loads before consent yourself.
Our guide on how to check cookies on a website shows the browser method.
Why is a copied generator text a risk?
A free generator gives you a generic text that suits an average website, not yours.
That’s exactly the problem.
The document reads professionally.
But it describes processing activities you may not carry out, and misses ones you do.
The typical mistakes
Four mistakes come back again and again:
- A webshop paragraph while you process no payments.
- Tools you don’t use named as processors.
- Your real tools missing: your specific CRM, email marketing platform or form software.
- Foreign legislation instead of the Belgian framework.
A privacy statement that doesn’t match reality isn’t only legally weak.
It’s also simply untrue towards your visitor.
The B2B cost: trust
That’s where the B2B cost lies.
A business buyer about to request a quote sometimes does read the fine print.
A sloppy or clearly copied privacy text sows doubt at exactly the moment you want to win trust.
It undermines the signal you build elsewhere on your site.
For example, on your about-us page, or via the trust signals that make a B2B site credible.
Rule of thumb: a generator is a fine starting point to see the structure. It’s never a finished product you publish unread.
How do you tackle a correct privacy policy for your website in practice?
Work backwards.
Don’t start with the text, but with an inventory of what your site really does with data.
Only once you’ve mapped that out do you write the two documents.
Step 1: Map out your data flows
Start with the forms. Then the tools. Then every integration.
Which fields do you ask on your contact page and in your conversion forms? Where does that data go?
Our guide to a GDPR compliant contact form shows what to ask and what to leave out.
Step 2: List your processors
Hosting, analytics, CRM, email tool, chat widget, form software.
These are the parties you must name in your privacy statement. Write them down with their country, so the EU question is answered too.
Processors need a contract too
Naming a processor in your statement isn’t the whole job. Article 28 of the GDPR says processing by a processor “shall be governed by a contract”.
For example, say your forms feed 4 tools: hosting, CRM, email platform and chat widget. Then you need 4 processing agreements, one per vendor.
Tip: most large SaaS vendors publish a standard data processing agreement. File it next to your inventory.
Step 3: Inventory your cookies and scripts
Which ones load, who places them, and are they essential or not?
This determines your cookie statement and the configuration of your consent banner. A cookie scanner run gives you the first list:
Our overview of website tracking helps you recognise each tag.
Step 4: Write or adjust the texts
Now you write. Use clear language, aligned with the Belgian and European framework.
Keep the two documents separate. Link both from the footer of every page.
Step 5: Have it reviewed legally
Then get a legal check. For the final wording, a lawyer or DPO is the right person, certainly with sensitive processing activities.
What we do, and what we don’t
Customer Impact is an agency, not a law firm: we don’t give legal advice.
What we do is build your website so the technology matches the text:
- your consent banner only fires trackers after consent
- your privacy and cookie statements are findable on your site
- both are readable for a visitor
That technical correctness belongs to the same foundation as accessibility. It’s too often treated as an afterthought.
The privacy statement also sits next to other required pages, such as your legal notice in Belgium.
Our list of mandatory website pages shows them all.
For the broader build process, see our guide on having a B2B website built and our web design agency.
Frequently asked questions about a website privacy policy
Do I need a separate cookie statement?
Yes, in practice. The privacy statement falls under the GDPR; the cookie statement falls under the ePrivacy rules, in Belgium Article 10/2 of the Data Protection Act.
Two legal bases. Two documents.
Can I use a free privacy policy generator?
As a starting point to see the structure, yes. Never as a finished product.
A generator text rarely names your own forms, tools and processors, which makes it inaccurate.
Do analytics cookies need consent in Belgium?
Yes. The Belgian DPA states that counting visitors is in principle not strictly necessary.
So analytics scripts may only fire after consent.
How fast must I answer a data request?
Without undue delay, and in any event within one month of receipt, under Article 12 of the GDPR.
The short summary
You need two documents:
- a privacy statement under the GDPR that honestly describes your data flows
- a cookie statement with a correctly working consent banner under the ePrivacy rules
The biggest pitfall is a generator text that doesn’t match what your site actually does. That’s legally weak, and it costs you trust with the business buyer you want to convince.
Decision rule: inventory first, text second, and make the technology keep the legal promises.
Don’t plan such an update as a standalone job. Bundle it into a broader plan: drawing up a website roadmap shows how.
Want your consent banner and statements checked against what your site really loads? Contact us.
Free website scan
Enter your website and get an automatic scan within minutes, with concrete technical and SEO improvements. No sales pitch.
We only use your details for your scan. No spam, unsubscribe anytime.